
मुख्य जानकारी
Security researcher Sammy Hajhamid has identified a software-based exploit affecting the Nintendo Switch 2. This vulnerability functions on firmware version 23.0.1 and allows for the execution of native code without requiring any hardware modifications or physical soldering to the console.
The exploit utilizes a chain reaction starting with SmileBASIC 4, a third-party application previously available on the original Switch. By leveraging a buffer overflow within this software, which has since been removed from the eShop, the researcher accessed a secondary vulnerability in the console's file management system.
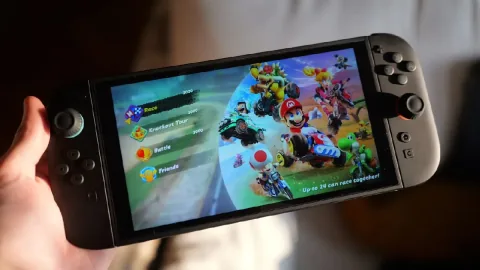
The researcher utilized AI-assisted tools to analyze the system and demonstrated the exploit by injecting modified files into Mario Kart World to replace character models. However, the hack is limited to running independent code and modifying existing games; it does not facilitate the execution of pirated software.
Technical limitations remain significant, as the exploit is tethered, meaning all modifications are erased upon restarting or powering off the device. Furthermore, the method does not grant kernel-level access or allow for the installation of permanent custom firmware, and the removal of the necessary software from the store prevents new users from replicating the process.


