
ข้อมูลสำคัญ
Two critical security vulnerabilities in the PHP programming language have forced game companies to initiate emergency maintenance and service suspensions. While the PHP development team released updated versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35 on the 21st to address these flaws, no hacking incidents have been reported yet.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, allow unauthorized attackers to execute arbitrary code on servers under specific conditions. Consequently, companies like Cygames and Sega scheduled emergency maintenance for their services on the 21st. Similarly, Final Fantasy 14 suspended its patch servers, preventing new logins to enhance security.
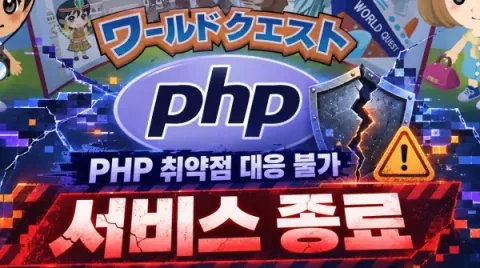
Choice of Games announced a temporary site suspension via its official forum to apply necessary patches. Meanwhile, the web game World Quest opted for a permanent service termination on the 21st. The developers cited the system's age and the inability to implement sufficient security measures as the primary reasons for this decision, prioritizing user data protection.
The PHP development team strongly recommends immediate updates to the latest versions to mitigate these risks. Despite the widespread operational disruptions, the industry remains focused on proactive maintenance to prevent potential exploitation of these server-side flaws.


